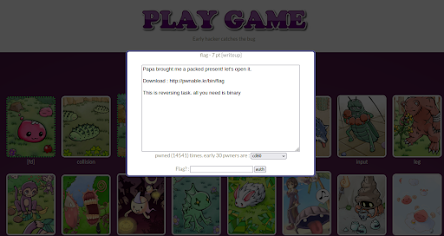
Description: "Papa brought me a packed present! let's open it."
This challenge from Pwnable.kr is a straightforward reversing task where the primary goal is to handle a packed binary.
Terminal: Identifying the UPX packer signature
Step 1: Identifying the Packer
Following the hint in the description about a "packed present," I checked the binary for common packing signatures. Running strings or checking headers confirms that the binary is packed with UPX.
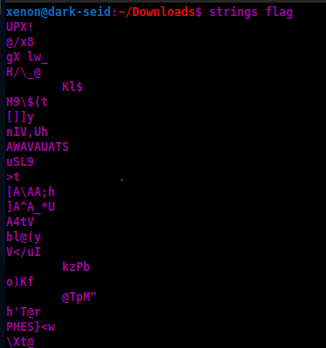
Terminal: Identifying the UPX packer signature
Step 2: Unpacking the Present
Since the binary is packed, we cannot perform standard static analysis or disassembly yet. We must use the UPX utility to unpack it first.
$ upx -d flag
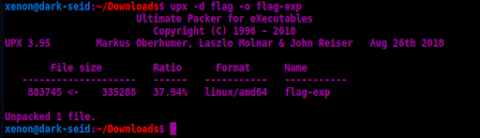
Decompressing the executable to its original state
Step 3: Disassembly and Flag Extraction
Once the binary is unpacked, it becomes readable. I prefer using Radare2 for disassembly. After loading the binary and analyzing it, we can look for where the flag is being handled in the data segment or being copied into memory.
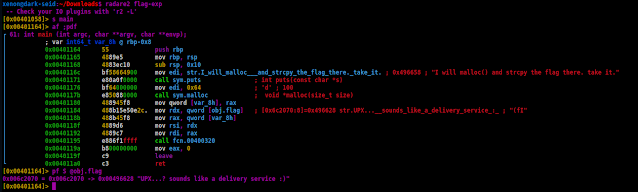
disassemble
By inspecting the code near the main or flag related functions, we can see the flag string clearly defined.
Conclusion
This challenge is a great reminder that the first step in any reversing task should be identifying if the binary is packed or obfuscated. UPX is a common packer that can be easily defeated once identified.