A stripped binary is a program compiled with a flag (like -s in GCC) that tells the compiler to discard debugging symbols. This makes reverse engineering more difficult because we lose the mapping between machine code and the original function names or variables.
Debuggers like GDB typically rely on two main mechanisms:
- Debug Information: Mapping between source code and machine instructions.
- Symbol Table: Associating functions and variables with their memory addresses.
Without these, GDB will often report: No symbol table is loaded. Here is how we bypass that to find a password in a stripped test binary.
I have created some c program for test purpose which is stripped.
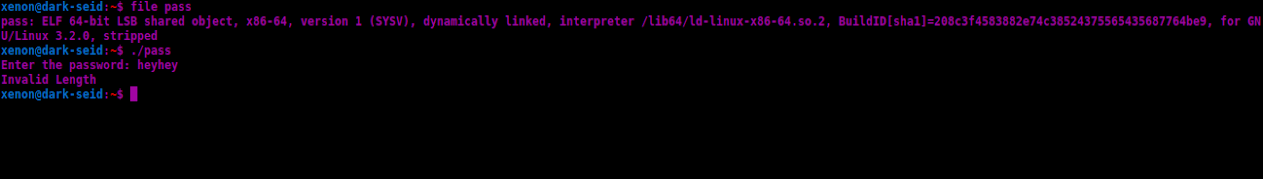
info and workflow
Step 1: The Symbol Obstacle
When we first open the stripped program in GDB and try to list functions or disassemble main, the debugger fails because it doesn't know where main starts.
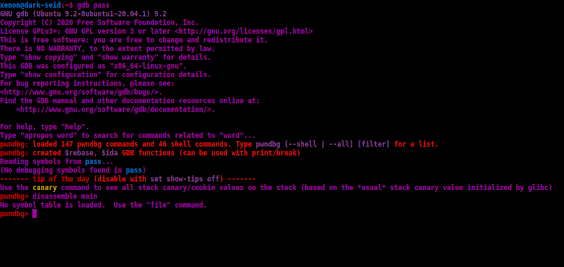
GDB
Step 2: Finding the Entry Point
Since we can't find main by name, we need to find the Entry Point. We can do this by running the program or using the info file command in GDB to locate the entry address.
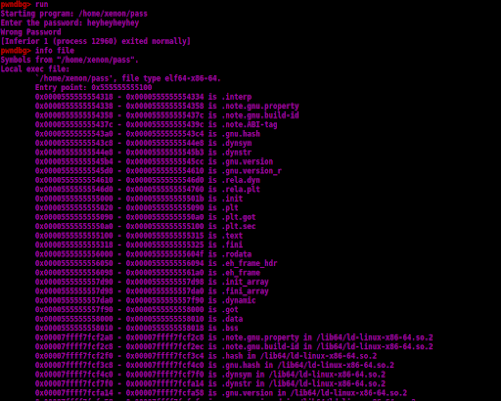
GDB
Step 3: Setting Breakpoints by Address
Once we have the address, we set a breakpoint at that location. To see the code, we disassemble from that address forward. For example, disassembling 200 instructions from the entry point gives us a clear view of the program's execution flow.
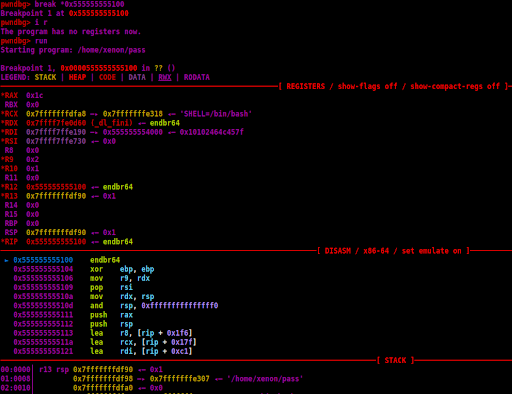
set brekapoint
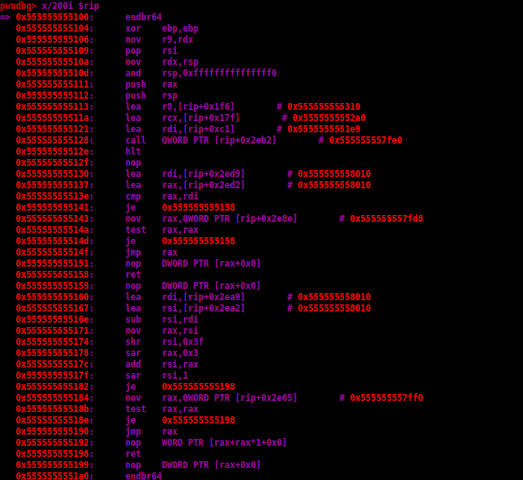
forward 200 instructions
Step 4: Analyzing the Logic
Looking at the disassembled code, we look for string comparisons or jump instructions. In this specific binary:
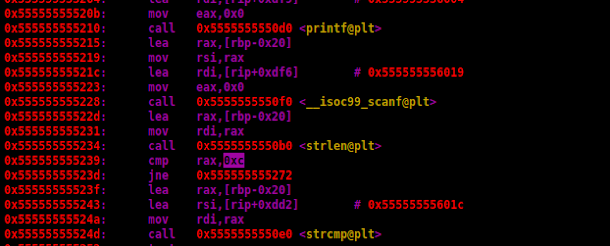
disassemble
- 0x555555555234: The program checks if the input string length is equal to 12.
- 0x55555555524d: It compares our input to an unknown hardcoded string.
- puts function: Depending on the comparison result, it prints "Welcome" or "Wrong password."
Step 5: Extracting the Password
By setting a breakpoint exactly at the comparison address (0x55555555524d), we can inspect the registers or the stack to see what our input is being compared against.
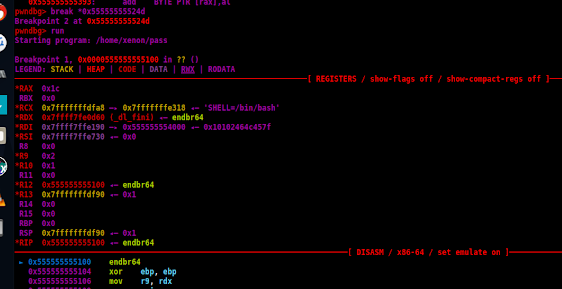
Inspecting memory at the comparison jump
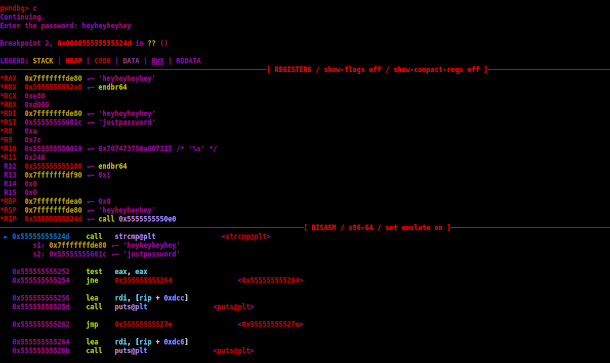
find the vaue in memory
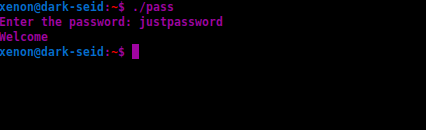
try password
Conclusion
Even without a symbol table, the logic of the binary remains the same. By finding the entry point and following the assembly flow to comparison jumps, we can recover secrets from stripped programs just as effectively as from standard ones.